Self-host your sensitive data
Run n8n air-gapped on your own servers. Self-host an AI stack with Ollama, Qdrant, and PostgreSQL with no external data transfer.
See llms.txt for all machine-readable content.
n8n is the processing layer for your security stack.
Build workflows and agents that gather context, close what
doesn’t need judgment — and log every step on the way.
Where our workflows make the work flow


500+ pre-built nodes for the apps you’re already logged in to.
Custom API connections for everything else.






Fully self-hostable, shield behind Slack or teams, expose nothing to the internet.
SSO/SCIM, SAML and LDAP encrypted secret store, version control, RBAC permissions.
Audit logs and log streaming to your SIEM, workflow history, real-time alerts, usage dashboards.


Workflows for the repeatable. Agents for the ambiguous. Humans for
the sensitive. Build all three in n8n — and own the layer that connects them.
Pull every alert into one queue. Enrich each one with the context that decides it — and let your AI agents make the call. Anything that doesn’t need human discernment gets closed before hitting your dashboard.
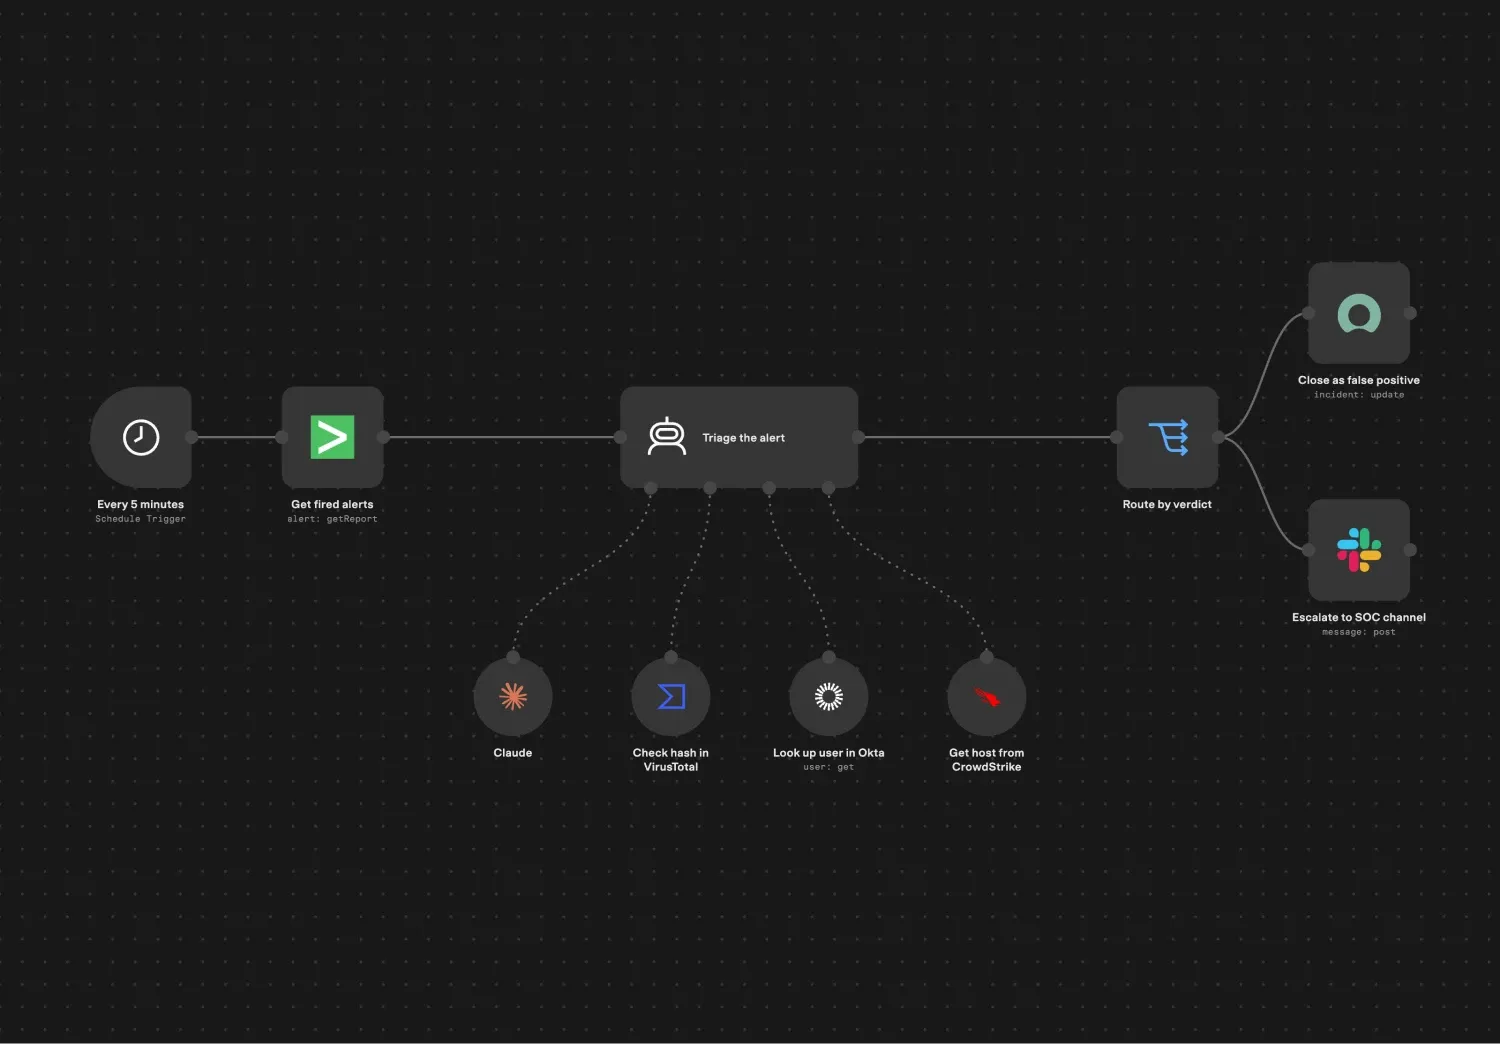
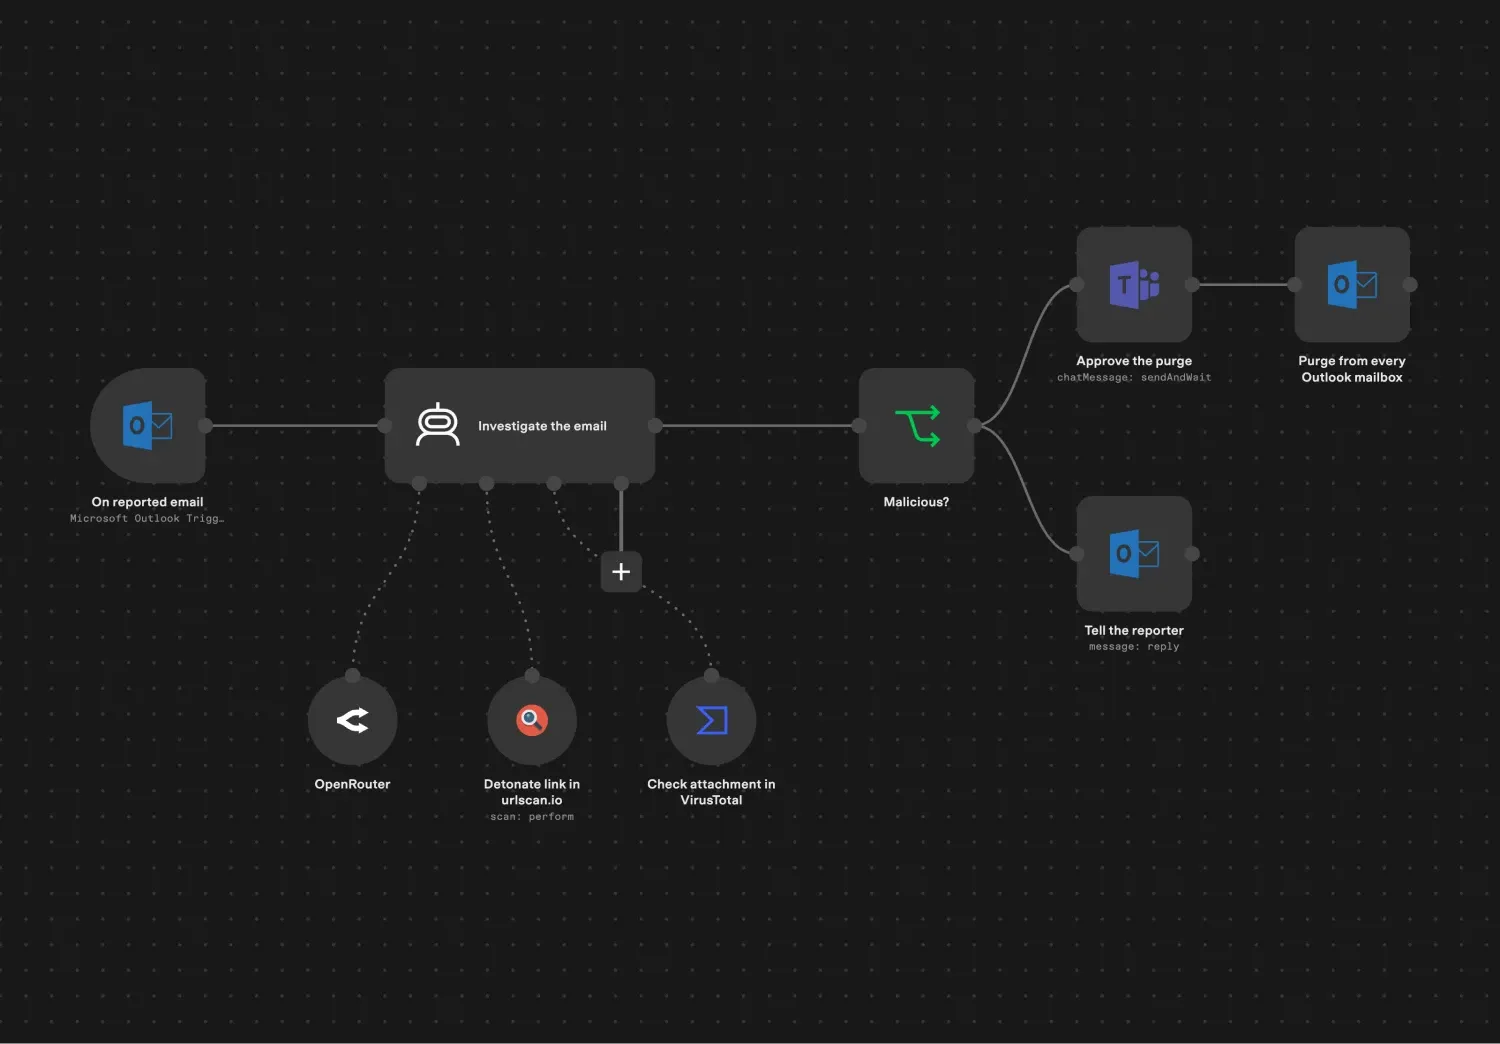
Avoid suspicious emails sitting around in Security’s inbox until they get opened. With n8n, the report becomes a workflow: Pull the headers and attachments, detonate whatever you need to. Pull the suspect message from every other mailbox.
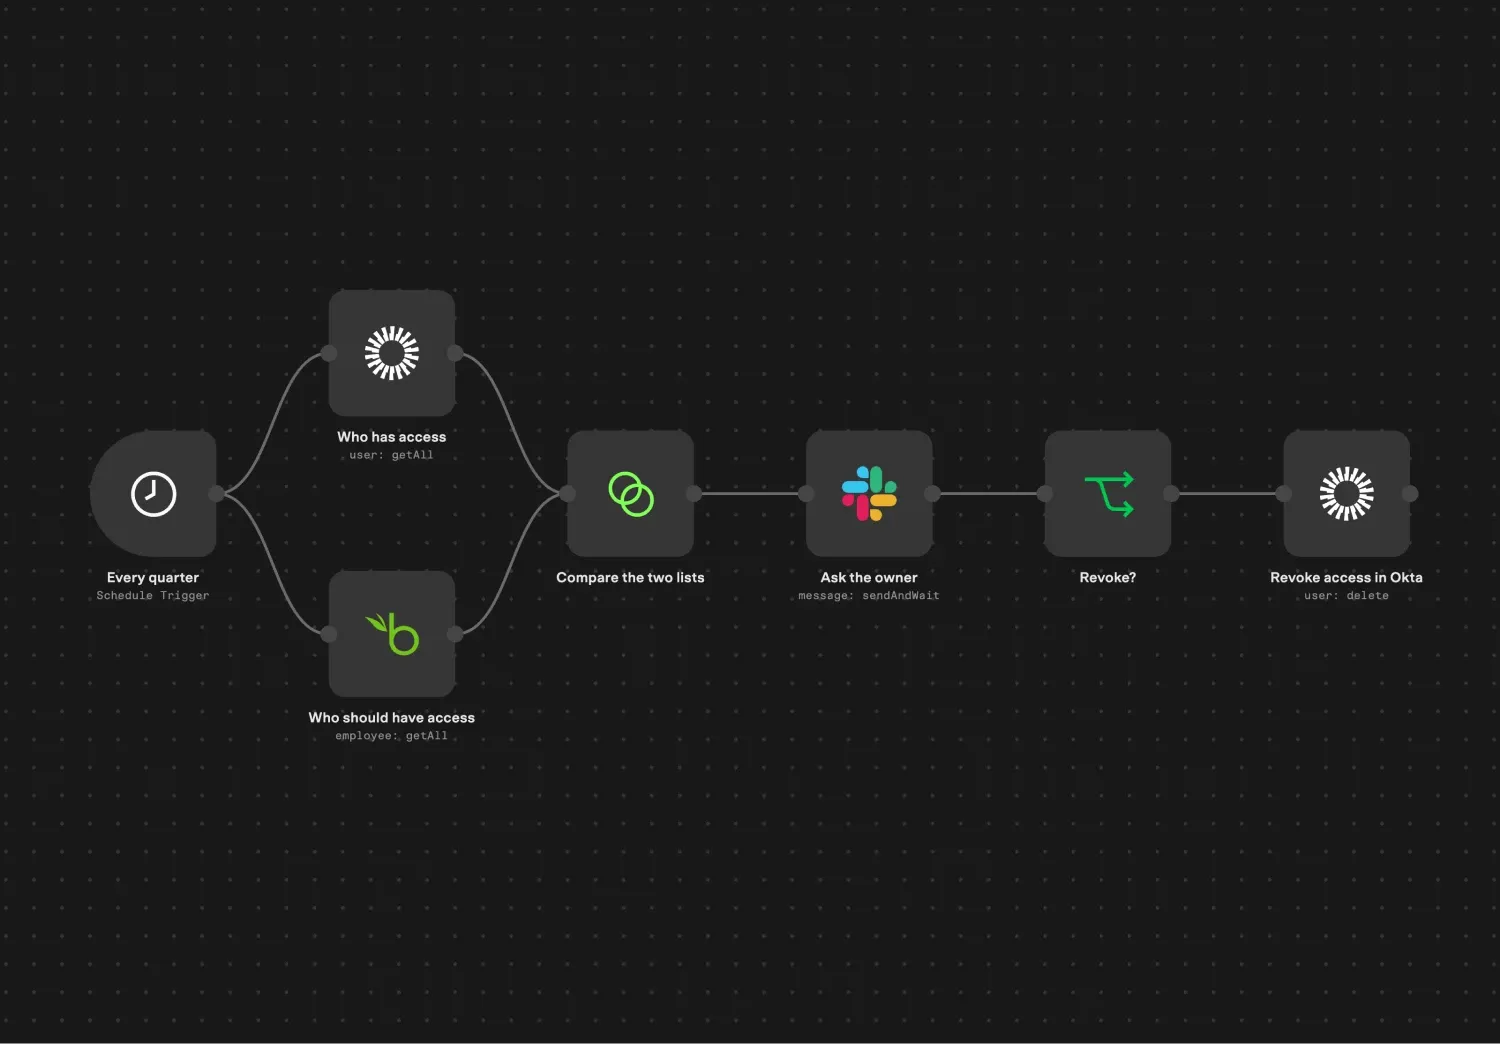
Does anyone know if the temp who left two months ago is still in Slack? It doesn’t matter. Run reviews on schedule. Ask each system who has access. Compare it with who should. Get a yes or no from someone who knows.
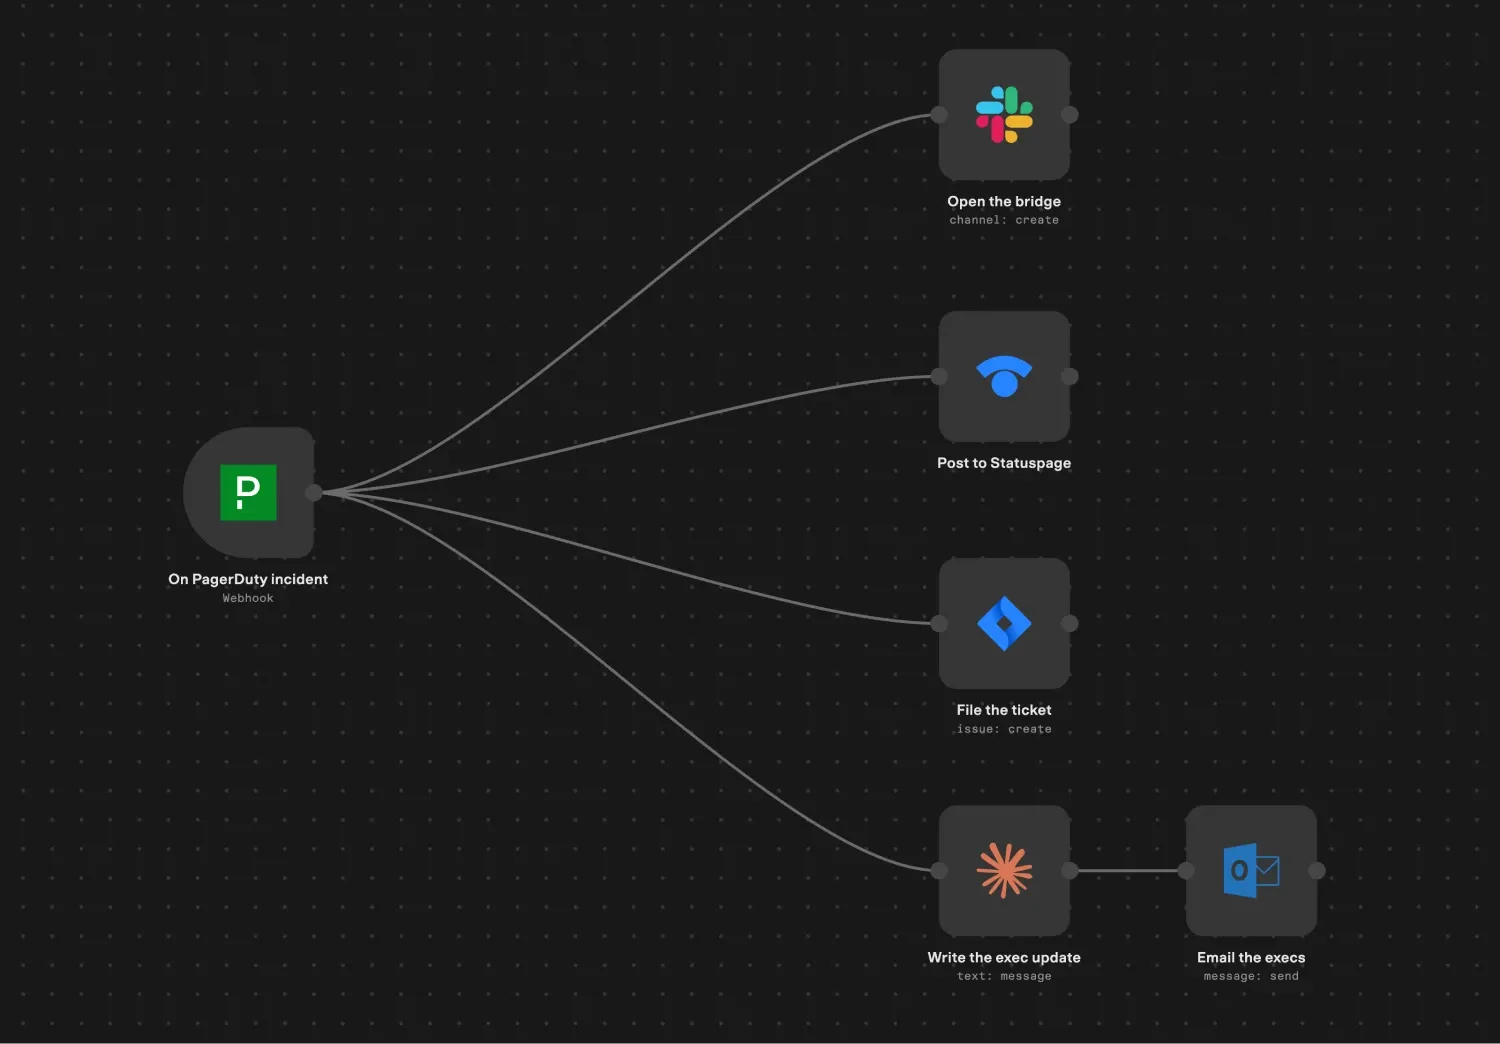
You don’t need 4 people writing the same thing whenever incidents open. In n8n, you open the bridge, write the status page, file the ticket, and write the exec update — all from a single trigger.
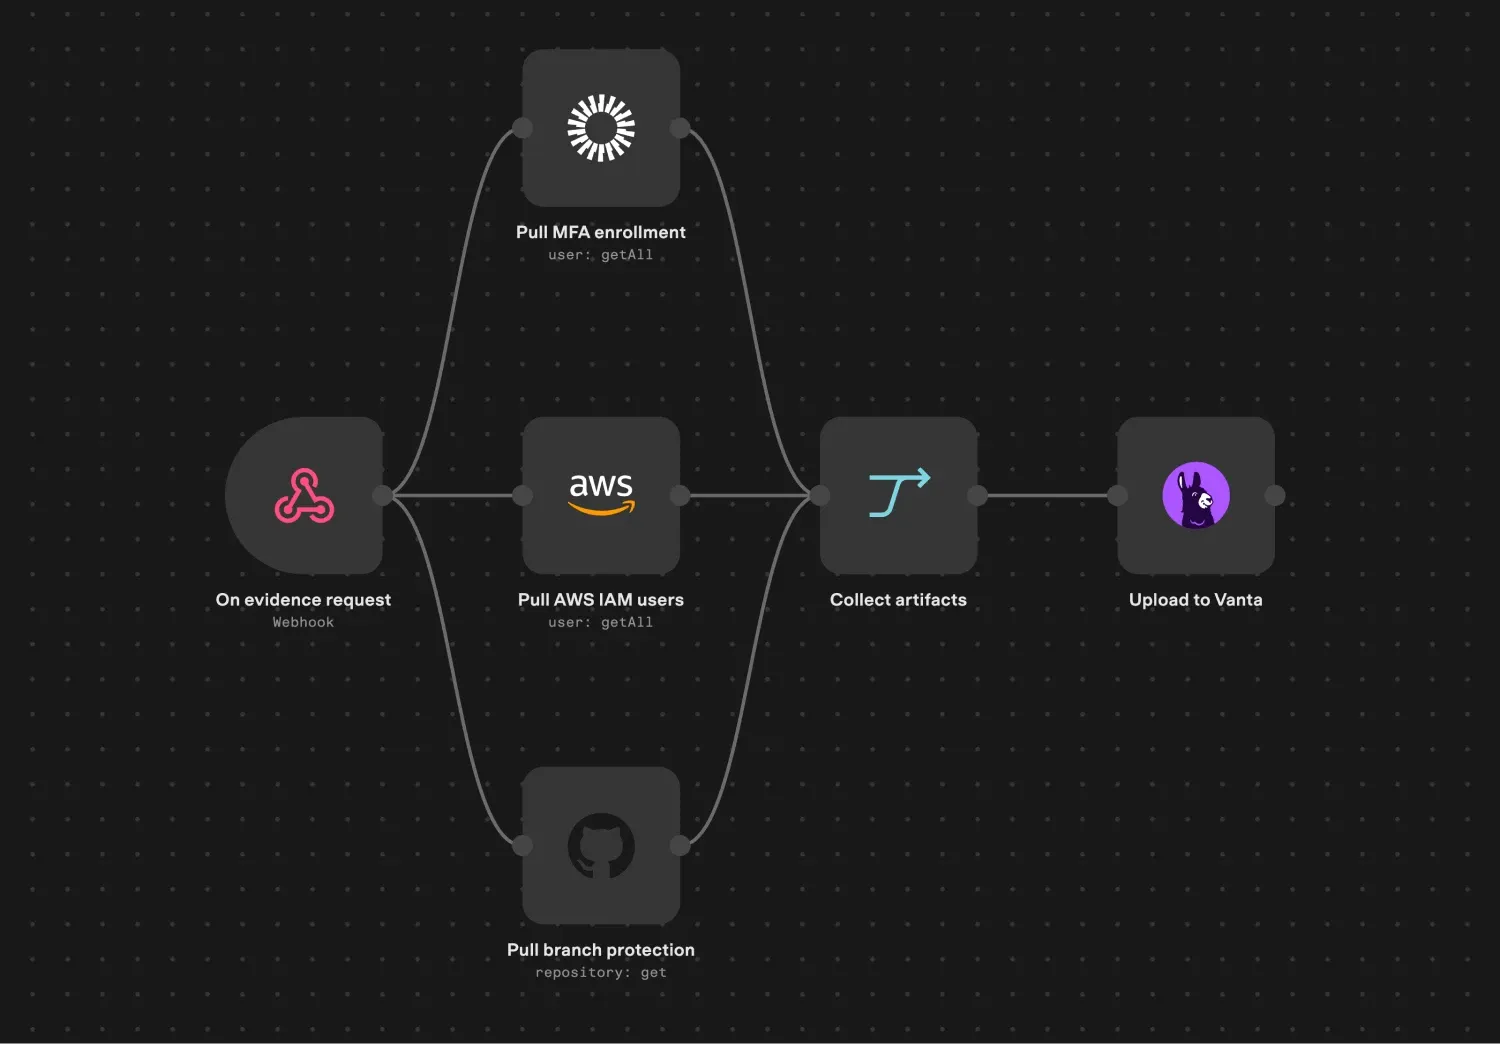
Screenshotting consoles shouldn’t eat up anyone’s week. Create workflows to collect the same artifacts from the same systems on a cadence you decide. All timestamped. And available where your auditor is already looking.
You have questions. Here are the answers you’re looking for:
I have found the holy grail of automation.
“We implemented security regulations with n8n, including logging and using a vault for credentials. Each team is scoped to their own project, ensuring they can only create workflows and access credentials within their own area, keeping all other teams' information secure.”
Run n8n air-gapped on your own servers. Self-host an AI stack with Ollama, Qdrant, and PostgreSQL with no external data transfer.
Open up any step to see what it does. Follow workflows visually in a UI that anyone on the team can read. Including the person who inherits it.
Sometimes no node covers exactly what your custom stack needs. So n8n lets you write the code yourself.
200+ templates for common workflows, including phishing triage,
IOC enrichment, access reviews, and evidence collection.


“n8n provides SOAR capability and workflows in a low-code model, as well as the ability to code for more complex workflows and integrations. It did everything that we wanted, all in one tool.”
Claire Van Hinsbergh
Cyber Operations Engineering Manager
“With n8n, everything stays in our server, we are in control. Self-hosting takes a lot off our plate in terms of compliance and complexity.”
Giuliano Ciccone
COO